How I work
Figure out what actually happened.
I like evidence, repeatable tests, and documentation another person can follow without scheduling a meeting with me. If I can’t explain why I reached a conclusion, I’m not done yet.

About me
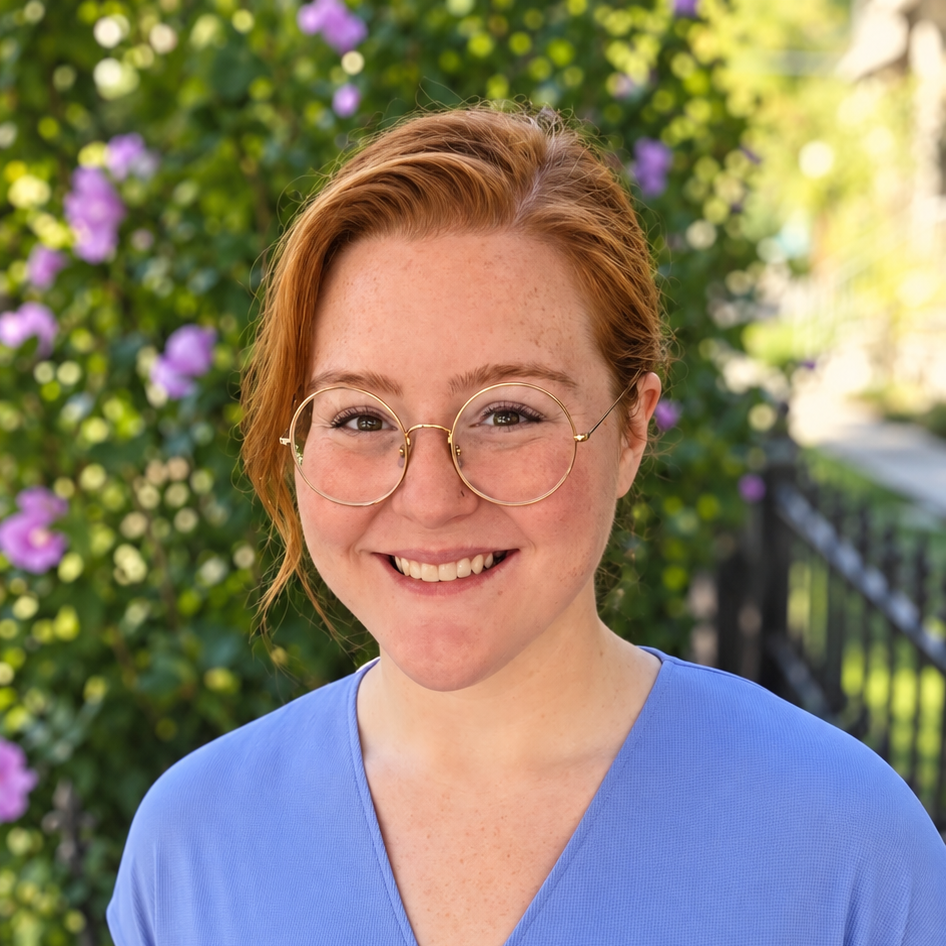
I’m a network security engineer with seven years across data center operations and cybersecurity. I like hard technical problems, clear documentation, cute clothes, and projects that let me take something apart until I understand it.
I learned infrastructure from the physical layer up in data centers, then spent four years working on security for physical-security and critical-environment networks. Most of my work has involved Palo Alto firewalls, Azure networking, ICS/OT environments, incident troubleshooting, and writing down what everyone needs to know next time.
Right now I’m building out my detection engineering and incident response work through synthetic incidents and a home lab. I’m using PastelIntel to publish the useful results instead of letting them disappear into another folder on my computer.
How I work
I like evidence, repeatable tests, and documentation another person can follow without scheduling a meeting with me. If I can’t explain why I reached a conclusion, I’m not done yet.
Why it looks like this
I grew up on a sheep farm, wear a lot of J-fashion, love old-computer interfaces, and drink an unreasonable amount of coffee.
I spent enough years trying to make myself look more conventional. This site is mine, so it looks like me.

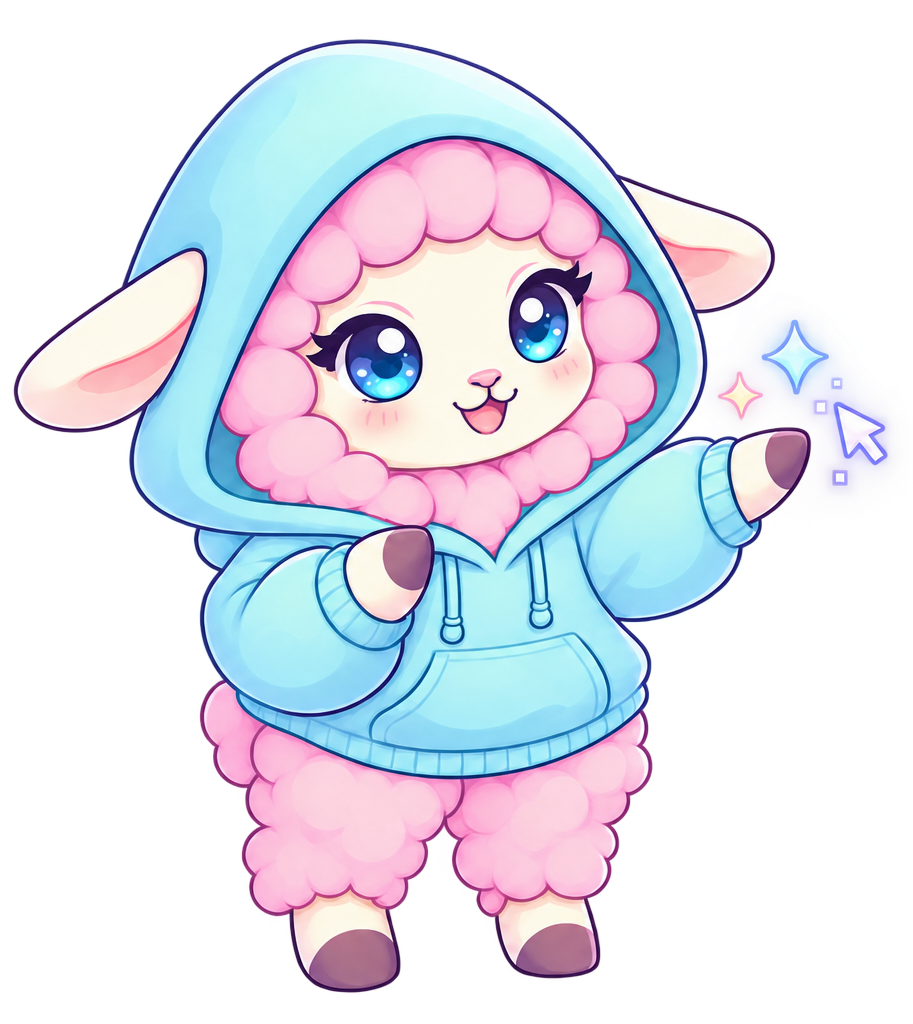
Pink wool, blue hoodie, and no respect for unlabeled cables.
Patch is the PastelIntel mascot. She’s a sheep because I grew up around them, and because cybersecurity has spent years using sheep as shorthand for people who don’t know better.
Security branding is full of wolves, skulls, black hoodies, and people trying very hard to look dangerous. Patch is my answer to that. She looks harmless, asks questions, and knows exactly what the logs say.
Her name covers security patches, patches of land, and patchy wool. That was too convenient to ignore.
I’d rather find the real problem than perform expertise.
Good documentation saves someone else from repeating the same miserable afternoon.
The details matter in detections, incident timelines, firewall rules, and apparently outfits.